Practical SOC skills · personal instructor guidance
From complete beginner to confident SOC analyst.
We teach you the work of an L1 SOC analyst, step by step. No practical experience needed.
Start with the basics. Learn to investigate alerts, analyse logs, decide when to escalate and write clear incident reports. Your instructor teaches you personally, helps when you get stuck and reviews your work as you build the confidence to investigate independently.
Have questions or unsure if this programme is right for you? Speak with your instructor about your goals, the lessons and how it all works.
Create your account, pay securely, then agree your class times with your instructor.
Guidance
One-to-one time with your instructor in the Complete Programme
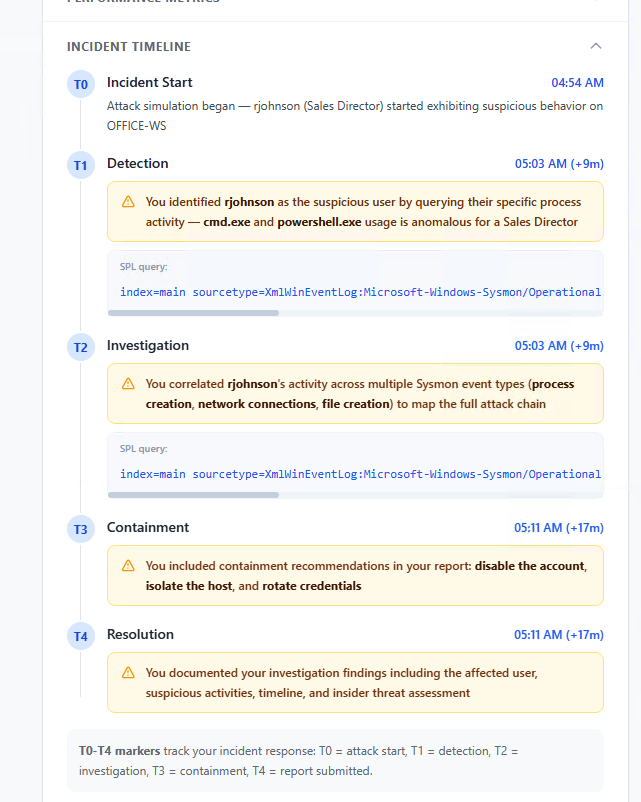
From inside the labFig. 01
An investigation, documented.
Detection → investigation → response
View full size An example lab record. Your investigation leaves a trail of queries, findings and decisions.
Hands-on learning, recorded on the platform.
Updated 17 September 2026
50+
Registered learners
26
Lab sessions completed
250+
Checkpoints completed
250+
Splunk queries run
How these totals are counted
Across real learner accounts. Completed lab sessions have a final score with all recorded checkpoints passed. Lab and checkpoint totals include repeat practice.
Your instructor
Saahil Chhabria
Founder, CymBytes
Six years building the cyber ranges enterprise SOC teams train on, at Cloud Range and RangeForce, a Cyberbit company. Every session is live with him, from the first search to the investigation review.
Six short recordings of a real lab session, narrated by your instructor. This is exactly what you sign up for: the dashboard, your own lab machine, the brief, Splunk, scoring and the report card.
Clip 0135 s · captions on
The dashboardWhere you land: an active lab session, your scores and the learning paths.
Clip 0235 s · captions on
Your own lab machineA Windows workstation and the lab portal, opened in the browser. Nothing to install.
Clip 0340 s · captions on
The briefWhat you are asked to investigate, the tasks, and the lab assistant if you get stuck.
Clip 0440 s · captions on
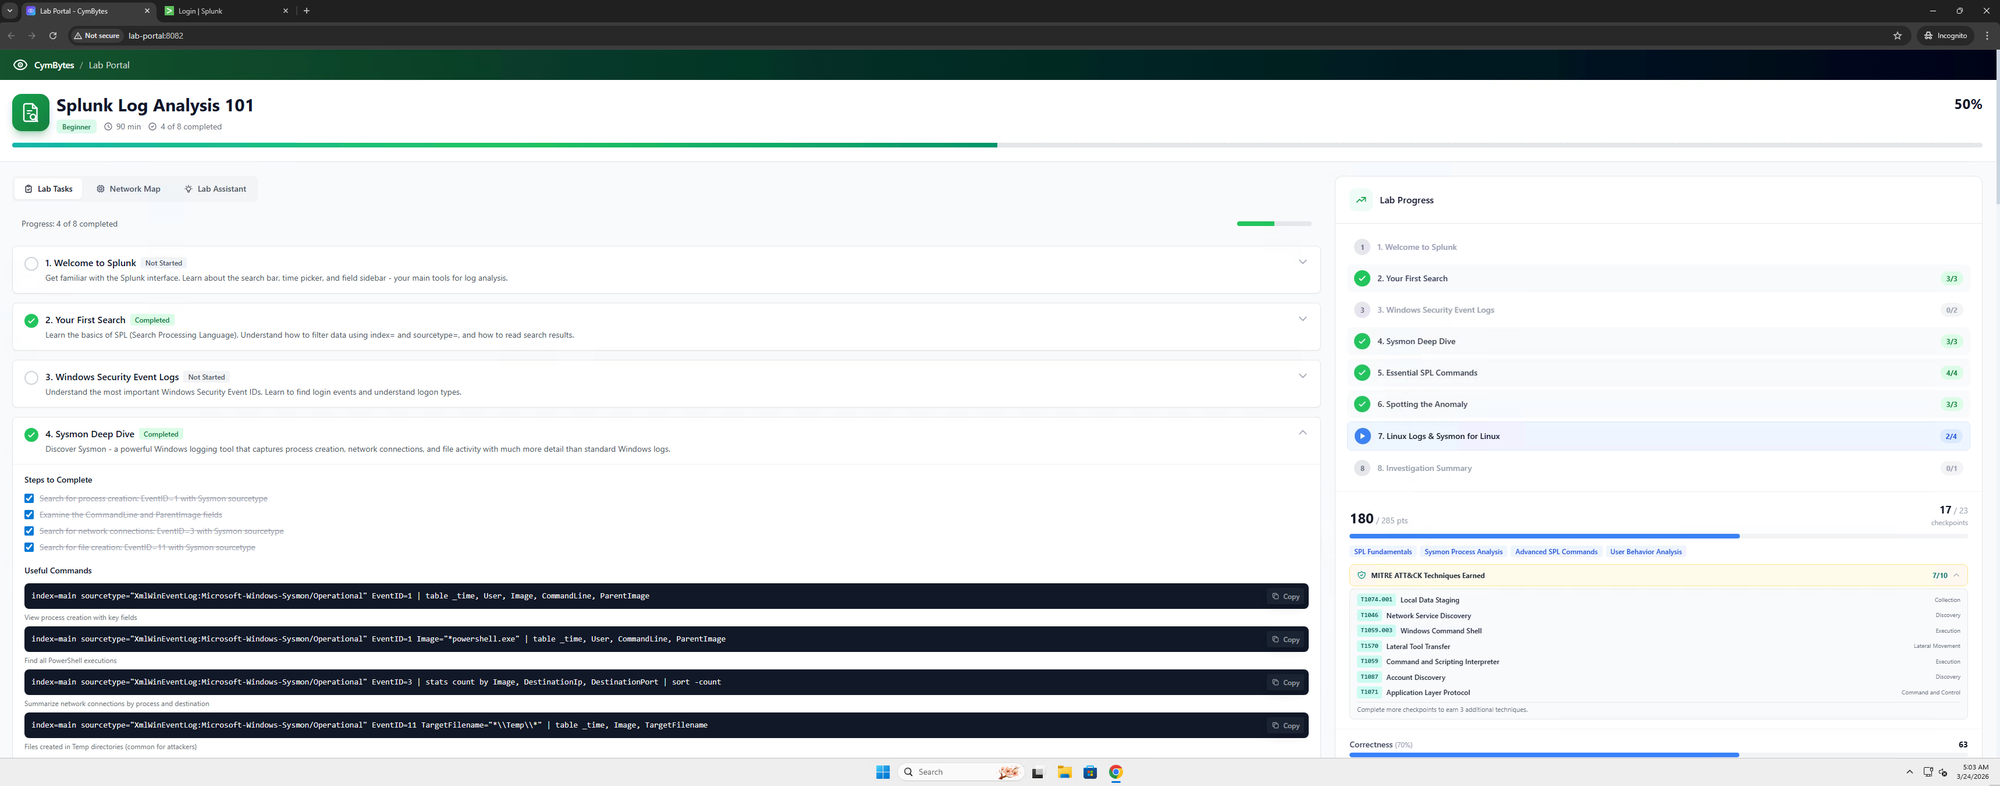
Into SplunkSearching Sysmon logs for the suspicious activity on OFFICE-WS.
Clip 0540 s · captions on
Scored as you goCheckpoints tick off as you find evidence, then your analytics across sessions.
Clip 0635 s · captions on
The report cardThe session report and certificate you can share.
Gopalan workshop · 16 September 2026
16learners completed all 6 introductory checkpoints
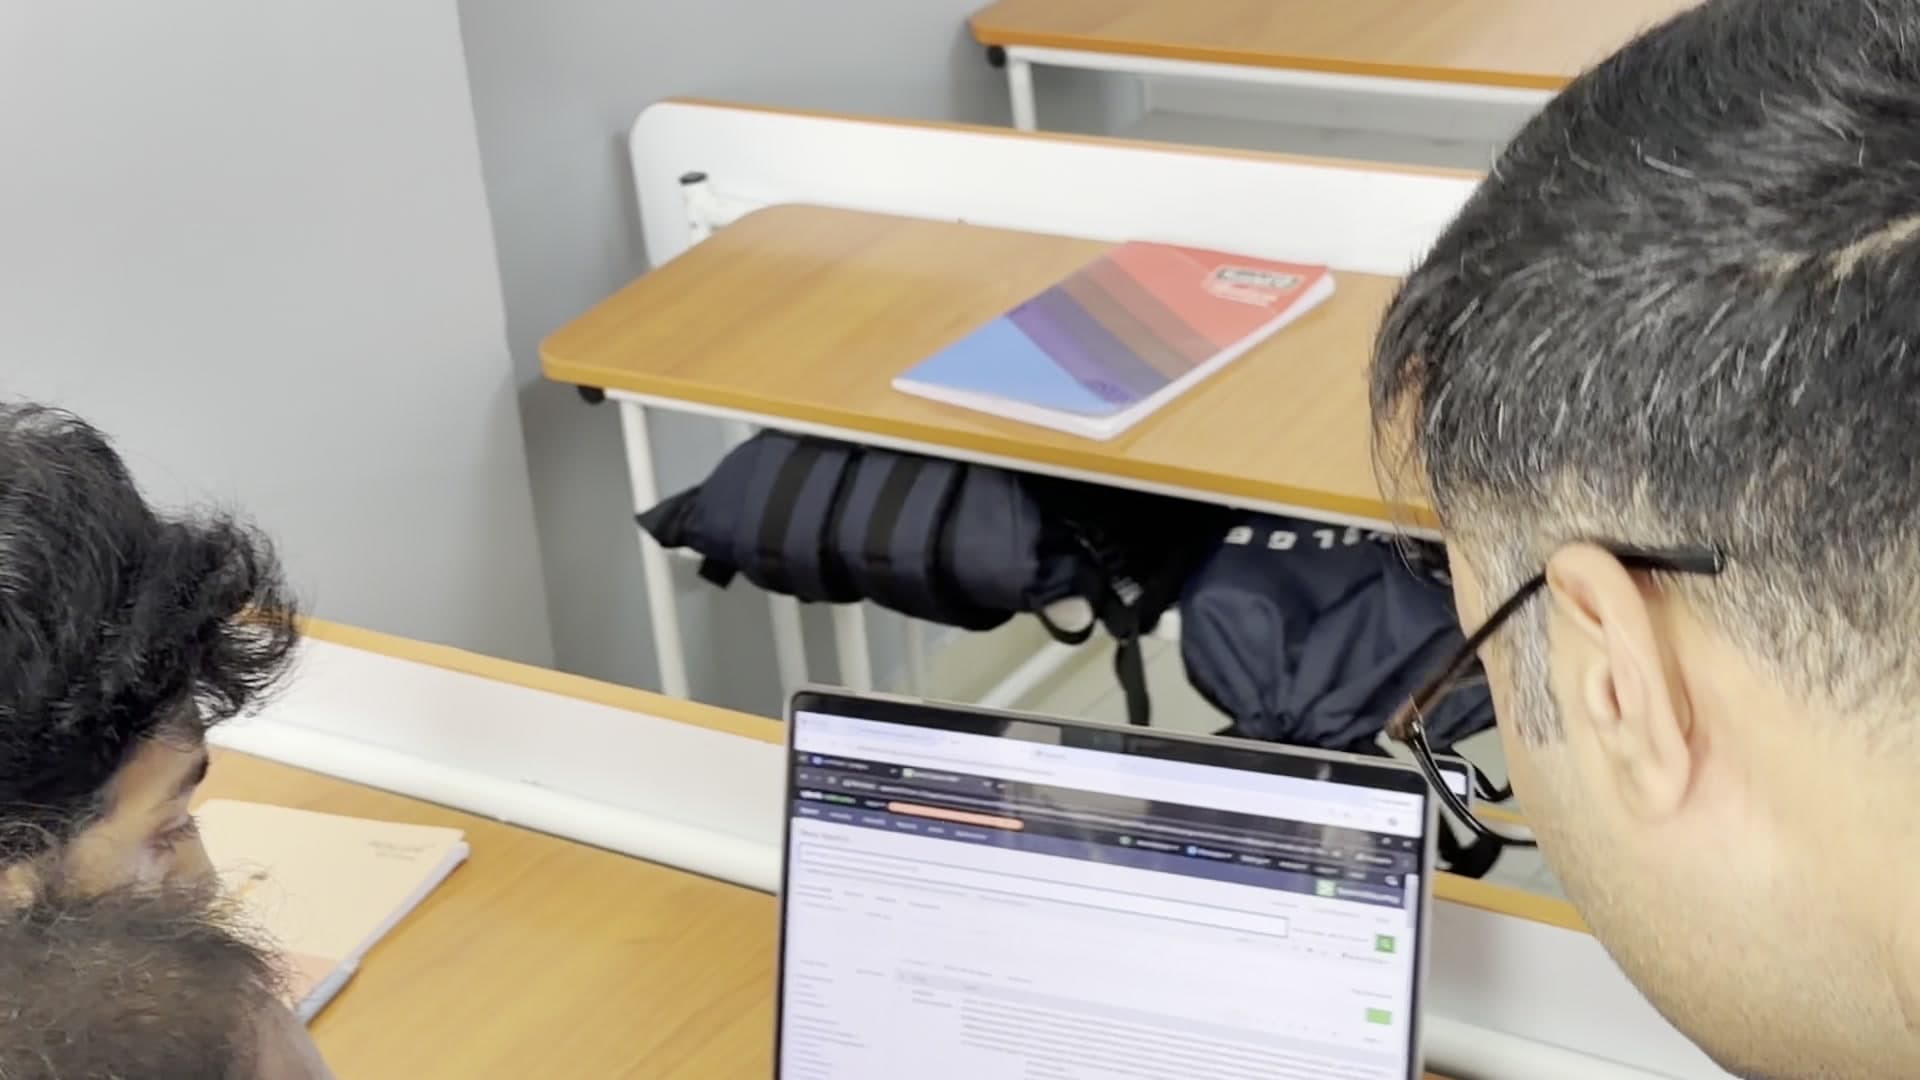
Inside a live classroom
Inside our Gopalan workshop.
See how students worked through their first Splunk searches with live guidance at Gopalan College of Engineering & Management.
When the interviewer says, “Walk me through an investigation you handled,” have a real example and the confidence to explain it.
Practise the work SOC analysts do in our hands-on labs: investigate suspicious activity, examine logs, decide whether an alert needs escalation, and write the handoff explaining your evidence and recommended next steps.
“Walk me through an investigation you did.”
Practise investigating suspicious activity in Splunk. Explain which logs you searched, how you connected the events, and what the evidence supported.
“How did you decide whether this alert was a false positive?”
Examine the account, host and surrounding activity. Practise testing an explanation and documenting what you could—and could not—conclude.
“What did you investigate before escalating, and what did you include in the handoff?”
Build a timeline, record affected accounts and hosts, and write a handoff with supporting evidence, your escalation reason and recommended next steps.
You'll learn and practise these skills in CymBytes labs—and build investigation reports and scored evidence you can confidently discuss in interviews. Describe this work as hands-on SOC lab experience: investigations you completed in our training environments.
In the Complete Programme, we help you build your hiring evidence and, with your permission, share it with relevant recruiters.
Who this is for
Turn your knowledge into practical skills.
Cybersecurity students and graduates with academic knowledge who want practical SOC experience.
IT support, NOC, network or sysadmin people moving into security.
Anyone with a certificate who freezes when an interviewer says "walk me through an investigation".
A learner's perspective
“Building practical learning environments that help people move from saying “I know the concept” to “I have actually worked with it” is an incredible effort worth supporting.”
Karthik DonepudiB.E. Computer Science graduate, aspiring SOC analyst · scored 98.5 on his first CymBytes lab
The curriculum
From your first search to a full investigation.
Start with the fundamentals, investigate simulated attacks and learn to explain your findings. You use the tools yourself, with help and feedback during your booked lessons.
Enrol first, then agree your class times
The standard programme runs over 5 weeks: two one-hour live lessons per week for weeks 1–4, followed by a final investigation and report review in week 5. Practise independently between lessons. Enrol and pay first, then agree your start date, exact lesson times and timezone with your instructor. The five weeks begin on your agreed start date; any change to this pace is agreed together.
Start with Splunk navigation, reading logs and writing your own searches. No practical SOC experience is needed.
Lesson 160 minutes
Splunk First Steps
Search a real Splunk index and answer the first questions a SOC asks of a log.
Included in the programme
Lesson 260 minutes
Reading Windows Logs
Read Windows security and Sysmon events well enough to spot a logon that should not be there.
Included in the programme
Lesson 360 minutes
SPL Detective
Write your own SPL to hunt across hosts and users instead of clicking through alerts.
Included in the programme
Lesson 460 minutes
Insider Threat Investigation
Run a full insider-threat investigation on a live domain: build the timeline, state the affected scope and write the escalation handoff.
Included in the programme
First capstoneInvestigate and write your incident report.1 lesson
Apply your foundation skills to malicious file execution, containment and reporting.
Lesson 560 minutes
Malicious File Execution
Capstone. Trace a malicious file from download to execution across endpoint and SIEM telemetry, then write the incident report. Submit your report for assessment toward the CymBytes SOC L1 Certificate.
Included in the programme
Build confidenceWork through harder investigations.4 lessons
Investigate different attack types, then review your reports and explain your decisions.
Lesson 660 minutes
Phishing C2 Detection
Hunt live phishing command-and-control traffic and prove the beacon.
Included in the programme
Lesson 760 minutes
AI Investigation Validation
Audit an AI analyst’s investigation and catch what it missed. Compare its reasoning with the evidence.
Included in the programme
Lesson 860 minutes
Autonomous APT Investigation
Chase an autonomous adversary through a kerberoasting attack chain, end to end.
Included in the programme
Lesson 960 minutes
Review and certificate claims
Report cards for every lab reviewed live. Review certificate eligibility and the evidence recorded across your attempts.
Included in the programme
Nine one-hour lessons, including investigation and report review. Practise independently between lessons using your included solo labs.
Your toolkit
Splunk Enterprise (real, licensed)
Windows Server domain controller + workstations
Windows Security and Sysmon telemetry
SPL search and detection writing
Live attacker infrastructure
MITRE ATT&CK mapping on every checkpoint
What you take away
Work you can put your name to.
An investigation you can explain, evidence behind your decisions and a record of your progress.
01Investigations you can explain
Keep your searches, incident timelines and reports. Practise explaining the evidence you found and the decisions you made in a SOC interview.
02Your portfolio + continued practice
Build a portfolio of scored labs and your written investigation. Download your evidence pack or choose to publish a link. Instructor feedback is available through your portfolio. Recruiter sharing is consent-based and does not guarantee an interview or placement. Lifetime access to eight included solo labs, with 12 launches per UTC calendar month.
03CymBytes SOC L1 Certificate
Submit an incident report and earn a final score of 70 or more in each of the five required foundation labs, with a plan that includes the certificate. Issued by CymBytes for assessed lab performance. Its public verification link records the completed labs and scores.
Training and assessment in lab environments. Completion does not establish a job level or guarantee employment. CymBytes does not provide placements.
One complete programme
Start from zero. Work towards your SOC role.
Learn directly with your instructor, get help when you are stuck and improve your investigations with feedback. Teaching and lab practice come together in one programme.
Personal teaching + practical labs
Complete SOC Investigation Programme
Your goal is to become a SOC analyst. We take you from your first log and Splunk search to investigating alerts, making response decisions and writing clear incident reports, with personal teaching and feedback from your instructor.
The standard programme runs over 5 weeks: two one-hour live lessons per week for weeks 1–4, followed by a final investigation and report review in week 5. Practise independently between lessons. Enrol and pay first, then agree your start date, exact lesson times and timezone with your instructor. The five weeks begin on your agreed start date; any change to this pace is agreed together.
The Complete Programme includes one-to-one time with your instructor. Start with the fundamentals, ask questions when you are stuck and receive feedback on your investigations and reports during your booked sessions.
9 one-hour live lessons, from the fundamentals to independent investigation and report review.
Eight solo labs, from your first Splunk search to malware, phishing C2 and advanced investigations.
Feedback on your searches, investigation decisions and written reports.
Build a portfolio and practise explaining your own lab work in SOC interviews.
Lifetime access to the included solo labs, with 12 launches per UTC calendar month.
Earn the CymBytes SOC L1 Certificate when assessment criteria are met.
Your one-time fee covers the included teaching, lab environments and software, assessment and CymBytes certificate when you meet its requirements. No separate lab, software or certificate fee for the included programme.
Base price in USD · INR checkout with UPI/cards for India; USD card checkout for overseas buyers.
No change-of-mind refunds once your first agreed live class starts; statutory rights apply. Read the terms
Have questions or unsure if this programme is right for you? Speak with your instructor about your goals, the lessons and how it all works.
Create your account. Choose Enroll Now and continue with Google or your email.
Pay securely. Pay US$300 once, or the quoted INR equivalent for India, through Razorpay.
Agree your class times. Your instructor contacts you after payment to arrange all nine lessons. Your five-week programme starts on the agreed date; practice labs are available after payment.
Everything opens in your browser. Bring a laptop and a stable internet connection.
Yes. Use Talk to Your Instructor to ask about your goals, the lessons or whether the programme is right for you. Your instructor will reply by email and can arrange a conversation or practical demo. No account or payment is needed.
Do I need any background?
No. Lesson 1 starts from your first Splunk search. If you can use a browser and follow instructions, you can start. Basic Windows familiarity helps.
Can I learn from the UK or another timezone?
The standard programme runs over 5 weeks: two one-hour live lessons per week for weeks 1–4, followed by a final investigation and report review in week 5. Practise independently between lessons. Enrol and pay first, then agree your start date, exact lesson times and timezone with your instructor. The five weeks begin on your agreed start date; any change to this pace is agreed together.
I already work in a SOC. Is this too basic?
The first five labs cover the foundations, ending with the malicious-file-execution capstone. Later labs practise C2 hunting, checking an AI investigation and tracking an autonomous adversary. The programme finishes with a review of your investigations, reports and progress. These are increasingly complex exercises; the course names describe training scope rather than a job level.
Will I get personal help during lessons?
The Complete Programme includes one-to-one time with your instructor. Start with the fundamentals, ask questions when you are stuck and receive feedback on your investigations and reports during your booked sessions. The programme includes nine one-hour lessons, including report review. You also practise independently between lessons.
Is this a recording of someone else’s lab?
No. Each student gets their own live Windows domain and Splunk server on cloud infrastructure. The attacks run inside your network during your session, and the logs you investigate are yours.
Do I need to install anything?
No. Everything opens in the browser. A laptop with a stable connection is enough.
Are there extra lab, software or certificate costs?
Your one-time fee covers the included teaching, lab environments and software, assessment and CymBytes certificate when you meet its requirements. No separate lab, software or certificate fee for the included programme.
What if I miss a session?
Bring a laptop and a stable internet connection. Ask questions during live class and use your portfolio to request feedback on a complete scored investigation. If you miss a class, contact the instructor to arrange a repeat or ask about recording availability.
What is the refund policy?
You may request a full refund before your first agreed live class starts. Once that class starts, we do not offer discretionary change-of-mind refunds. If we cannot agree a suitable timetable, we will refund your payment in full. Your statutory cancellation rights and remedies if we fail to deliver as promised are unaffected. Details are on the refund policy page. Read the refund policy.
What does completion qualify me for?
The goal is to prepare you for the practical work of an L1 SOC analyst: investigate alerts, analyse evidence, recommend a response and communicate your findings clearly. Training and assessment in lab environments. Completion does not establish a job level or guarantee employment. CymBytes does not provide placements. The certificate records the required lab assessments, and employers make their own hiring decisions.
From beginner to SOC analyst
Let’s talk about your SOC goal.
Discuss your experience, your SOC career goal, and how the programme can help you get there. Enrol online, then agree suitable class times with your instructor. You can speak with your instructor before deciding.
Complete Programme · US$300 one-time · 5 weeks · nine live lessons