Explore an unfamiliar SIEM
Splunk First Steps
Evidence to build: Identify the available sources, choose a time range and save the events that answer your question.
SOC Foundations Bootcamp · live with Saahil Chhabria
Applying for your first SOC role? Practise Splunk searches, Windows-log analysis and an insider-threat investigation. Build a case study you can explain with confidence.
₹1,999 one-time · no renewal
Learn to investigate Windows activity in Splunk across four live evenings. Complete scored labs and build an incident report you can explain in interviews.
1. Search Splunk
Find the right index, inspect events and answer questions with evidence.
2. Read Windows logs
Interpret logons, process activity and Sysmon events.
3. Write SPL investigations
Compare hosts and users, build timelines and test a hypothesis.
4. Explain an incident
Investigate an insider threat and write findings with a containment recommendation.
Submit an incident report and earn a final score of 70 or more in each of the four required foundation labs, with a plan that includes the certificate.
Paid-program commitment: we help you build hiring evidence from your scored investigations and written case studies. When it is ready, and only with your permission, CymBytes will share it with relevant recruiters. This is included only in paid programs.
Build a portfolio of scored labs and your written investigation. Download your evidence pack or choose to publish a link. Instructor feedback is available through your portfolio. Recruiter sharing is consent-based and does not guarantee an interview or placement.
Bring a laptop and a stable internet connection. Ask questions during live class and use your portfolio to request feedback on a complete scored investigation. If you miss a class, contact the instructor to arrange a repeat or ask about recording availability.
Job-to-lab checklist, investigation worksheet, interview debrief prompts and one instructor-assigned follow-up exercise with portfolio feedback. Practice uses your included labs and monthly launch allowance. See the preparation guide.
Lifetime access covers the included solo practice labs; Operation Loki, where included, is instructor-led and scheduled. Live teaching covers the booked sessions; it is not an unlimited live-class subscription. Monthly launches reset on the first day of each UTC calendar month.
For students, graduates and people moving from IT into security. You need a laptop, a reliable connection and time to practise after class. Splunk and the lab machines open in your browser.
The four lessons repeat in a rolling cycle. You can join at the next lesson; check its preparation below. Prefer to start at lesson one? Ask the instructor before enrolling.
Saahil teaches the sessions live, drawing on six years building cyber ranges at Cloud Range and RangeForce. Meet your instructor.
Live teaching spans four evenings. Independent practice and portfolio completion are at your pace; your included labs do not expire.
For students, graduates and career changers who need a starting point in Splunk. Use these exercises to practise foundational responsibilities in trainee and junior SOC job descriptions, then check each employer’s remaining requirements.
Bring a role you want to apply for. Match its responsibilities to these labs, record your evidence and identify the gaps. A curriculum match is not an employer endorsement.
Splunk First Steps
Evidence to build: Identify the available sources, choose a time range and save the events that answer your question.
Reading Windows Logs
Evidence to build: Explain the logon or process events you selected, the relevant fields and what they can establish.
SPL Detective
Evidence to build: Write and explain your own searches, compare activity and test a benign explanation.
Insider Threat Investigation
Evidence to build: Build a timeline, state the affected scope and write a concise evidence-backed handoff.
These four labs establish a foundation. Malware execution, phishing-related C2 and the Loki team hunt belong to the higher offers. Check networking, Linux, EDR, other SIEM products, shift procedures and any required qualifications separately.
Save your case study in My portfolio, declare the help you used and submit for instructor feedback. Keep source events and queries with your conclusions. Publish only work you completed and can explain.
Download this offer’s preparation workbook →Rehearse using your own evidence. Bring a question to the booked class; debrief practice uses existing teaching time, with written feedback available through your portfolio.
After the four labs, ask for a changed Windows or insider-threat investigation question. For example, investigate whether a suspicious pattern is isolated, and explain what would support a benign explanation. Your instructor assigns the actual scope and evidence window; attempt it without a walkthrough, then submit your reasoning for feedback.
One instructor-assigned follow-up is included. Use an included lab and your normal monthly launch allowance. Append “Follow-up assessment” to the matching case study, preserving the original. Record the assignment, date and any assistance; mark mixed if guided and independent work coexist.
This is instructor-reviewed practice, not a new automatically scored scenario or a proctored exam. Feedback covers evidence, method, uncertainty and handoff. Certificate criteria are unchanged; no extra live session is included.
Use “Practical projects” or “SOC lab investigations” and replace these placeholders with your completed work.
Investigated [Windows activity / insider-threat scenario] in a simulated enterprise lab using Splunk. Wrote [searches], established [supported finding] and documented a timeline and escalation recommendation. Evidence: [optional report link].
Describe this as practical lab or project experience. Training does not count as employment, replace required years of experience, or guarantee an interview or a job. Employers decide eligibility and selection.
Loading your next available classes…
Your evidence pack combines platform-recorded results with a case study you write: the question, SPL searches, timeline, findings and recommendations. You choose whether to publish it.
A certificate becomes available after you meet the assessment criteria in all four foundation labs. Training and assessment do not guarantee an interview or a job.
See students working through their first Splunk exercise →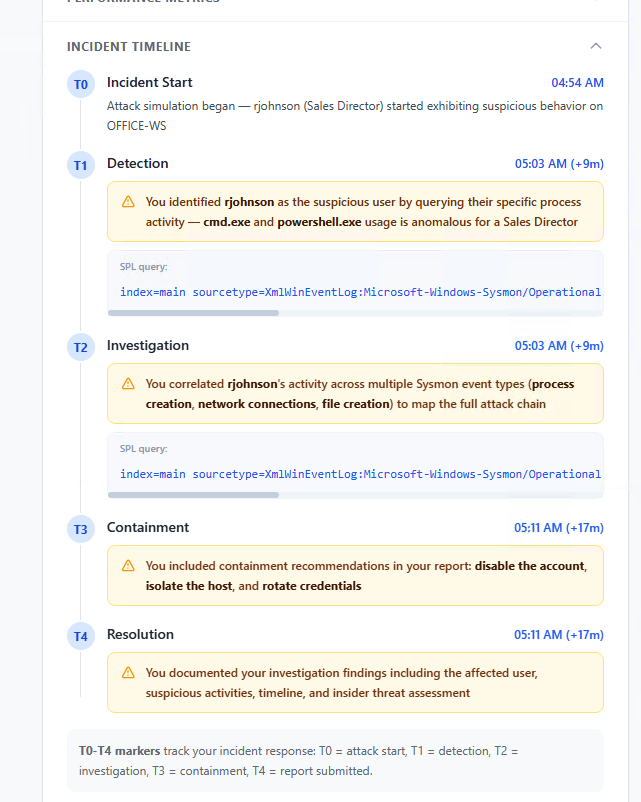
Add malware execution and phishing-related C2 with the SOC Investigation Course for ₹4,000 more. For AI validation, an APT investigation and a team hunt, explore the Complete programme.
Full refund, no reason needed, any time before your third live session. Sessions count from your first scheduled session after purchase, whether or not you attend. After that, fees are non-refundable. Your checkout shows the exact deadline.
Four included live classes; repeat attendance is arranged with the instructor. Ask about recording availability if you miss a class. Lab practice has a monthly launch allowance.